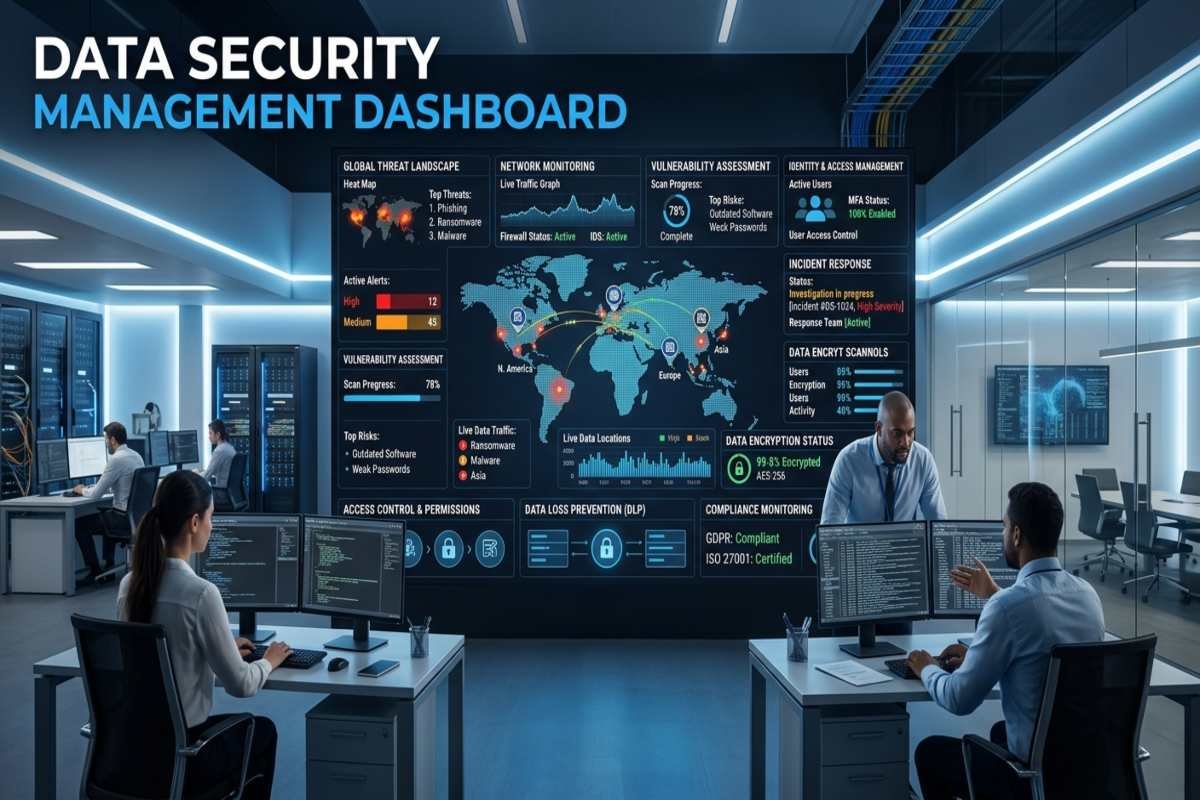
Data security management helps organizations protect sensitive information from unauthorized access, data breaches, accidental loss, and cyberattacks. It combines security policies, access controls, encryption, monitoring, backups, and employee training to keep information confidential, accurate, and available when needed.
For businesses, effective Data Security Management is not just an IT responsibility. It is an ongoing process that protects customer records, financial information, intellectual property, cloud environments, and AI powered applications while supporting business continuity and regulatory obligations.
What Is Data Security Management?
Data security management is the process of identifying, classifying, protecting, monitoring, and securely disposing of information throughout its lifecycle. It helps businesses determine who can access data, where information is stored, how it is shared, and how it can be recovered after an incident.
- Classifying data according to sensitivity and business value.
- Applying least privilege access and multifactor authentication.
- Encrypting sensitive information at rest and in transit.
- Maintaining secure backups and testing recovery procedures.
- Monitoring suspicious activity and investigating security alerts.
- Training employees to recognize phishing and social engineering.
- Reviewing third party vendors, cloud services, and AI systems.
Why Is Data Security Management Important?
Organizations store information across laptops, databases, cloud platforms, business applications, and third party services. Without clear security controls, confidential data can be exposed through stolen credentials, misconfigured storage, malicious insiders, software vulnerabilities, or human error. Effective management reduces the likelihood and potential impact of data exposure. It also helps organizations maintain customer trust, support applicable privacy requirements, and recover more efficiently when security incidents occur.
- Confidentiality: Only authorized people and systems can access information.
- Integrity: Information remains accurate and protected against unauthorized changes.
- Availability: Authorized users can access information when business operations require it.
These principles work together. A company that encrypts every database but cannot restore its critical records after ransomware still has a serious data security weakness.
What Are the Best Practices for Data Security Management?
The most effective approach combines technical safeguards, documented procedures, employee awareness, and regular testing. The following practices help organizations build a practical, layered defense.
Identify and Classify Sensitive Data
Start by discovering what information your organization collects, where it is stored, who uses it, and how long it must be retained. Include customer details, employee records, payment information, business documents, API keys, source code, and AI training data where applicable.
Classify information into categories such as public, internal, confidential, and restricted. Apply stronger controls to highly sensitive records instead of treating every file as equally important.
Apply Least Privilege Access Controls
Employees, applications, and automated systems should receive only the permissions needed to perform their assigned tasks. Excessive permissions increase the damage that compromised accounts or malicious insiders can cause.
Use role based access control, multifactor authentication (MFA), strong authentication policies, and periodic access reviews. Remove access promptly when employees change roles or leave the organization.
Encrypt Data at Rest and in Transit
Encryption helps prevent unauthorized parties from reading information if storage devices, files, or network traffic are exposed. Effective Code Security practices include using established encryption protocols for stored data and secure connections for data moving between users, applications, and servers.
Protect encryption keys separately from the information they secure. Restrict key access, rotate keys according to documented policies, and establish recovery procedures so legitimate users do not lose access to encrypted records.
Secure Cloud Storage and Business Applications
Cloud security misconfigurations can expose sensitive records even when the underlying cloud provider operates securely. Review storage permissions, database access, public sharing settings, identity policies, and application configurations.
Use centralized logging, approved configurations, and automated checks where practical. A documented Cloud Security Assessment can help identify weaknesses in cloud resources, application permissions, and data flows before they become serious incidents.
Maintain Secure Backups and Test Recovery
Backups help organizations recover from ransomware, accidental deletion, hardware failures, and other disruptive events. However, backups are useful only when they are complete, protected, and recoverable.
Maintain offline or otherwise isolated copies of critical data, restrict backup administration, and encrypt backup files. Test restoration regularly and establish recovery time objectives (RTOs) and recovery point objectives (RPOs) based on business needs.
Train Employees to Recognize Phishing
Employees may accidentally disclose credentials or confidential information after receiving convincing fraudulent messages. Training should explain how to verify unexpected requests, inspect suspicious links, report unusual attachments, and confirm payment or account changes through trusted channels.
Include Spear Phishing in awareness training because targeted messages may imitate colleagues, suppliers, or executives. Reviewing realistic Phishing Email Examples can help staff recognize suspicious sender addresses, unexpected requests for sensitive data, and unusual urgency.
Monitor Systems and Detect Suspicious Activity
Collect security logs from databases, cloud services, identity providers, and critical applications. Look for unusual downloads, repeated login failures, unexpected permission changes, and access to sensitive records outside normal business patterns.
AI Threat Detection tools can help identify suspicious behavior across large volumes of activity, while AI Threat Intelligence can provide context about emerging attack methods. These technologies support investigations but should not replace reliable logging, human review, and tested incident response procedures.
Manage Third Party and Supply Chain Risks
Vendors may process customer records, provide software components, or access internal systems. Assess their security practices before granting access, document contractual responsibilities, and review their permissions periodically.
Effective Supply Chain Planning should account for cybersecurity dependencies, including software suppliers, cloud providers, data processors, and AI services. Maintain an inventory of important dependencies, evaluate security updates, and establish procedures for responding when a supplier experiences a breach.
Protect AI Systems and Sensitive Data
Generative AI applications can introduce additional data exposure risks when they connect to internal documents, databases, external APIs, or business tools. Employees may also submit confidential information to AI services without understanding how their data is handled.
Organizations should establish approved use policies, minimize the information sent to AI systems, restrict access to connected data sources, and review retention and training settings. Relevant OWASP LLM Security Risks include prompt injection, sensitive information disclosure, data and model poisoning, and supply chain vulnerabilities. These risks are covered in the OWASP GenAI Security Project.
Create an Incident Response Plan
A data security incident requires coordinated action, not improvised decisions. Document how employees report incidents, who leads the response, how affected systems are isolated, and how evidence is preserved.
Your plan should also cover recovery, stakeholder communication, and applicable notification obligations. Conduct tabletop exercises to test scenarios such as stolen credentials, exposed cloud storage, ransomware, and unauthorized access through a third party service.
How Can Businesses Implement Data Security Management?
A practical implementation plan helps organizations move from general security goals to measurable improvements. The NIST Cybersecurity Framework 2.0 offers a useful structure for understanding, prioritizing, and managing AI Cybersecurity risks. Identify sensitive data, critical systems, existing controls, vulnerabilities, and third party access. Enable MFA, remove excessive permissions, encrypt sensitive data, and secure backups.
Assign responsibility for data access, retention, vendor reviews, incident reporting, and recovery. Review alerts, test restoration, reassess risks, and measure whether security controls work as intended. Start with the systems holding the most sensitive information or supporting the most critical business operations. Small businesses can implement these measures progressively instead of purchasing complex security platforms before understanding their actual risks.
Common Data Security Management Mistakes to Avoid
Even organizations with security software can leave significant gaps when policies and daily practices are poorly maintained.
- Excessive Access: Old accounts and unnecessary permissions can expose confidential records.
- Untested Backups: A successful backup message does not prove that data can be restored.
- Incomplete Employee Training: Employees need practical guidance for reporting suspicious activity.
- Uncontrolled Data Sharing: Public links and unauthorized applications can bypass established controls.
- Ignoring AI Integrations: Connected AI tools may access more information than their tasks require.
- Weak Vendor Oversight: A supplier’s access can remain active long after a project ends.
A useful Cybersecurity Checklist should assign an owner and review date to each control, rather than simply recording whether a security tool has been purchased.
Conclusion
Effective Data Security Management depends on knowing what data your organization holds, limiting who can access it, protecting it with appropriate technical controls, and preparing for incidents. Regular reviews, tested backups, employee training, and responsible AI use make these protections more reliable.
For additional cybersecurity guidance, AiSecMaster readers can explore related resources on LLM security best practices and source code security. Start by assessing your most sensitive data and addressing the highest priority risks before expanding your security program.
Frequently Asked Questions (FAQs)
What is the full form of data security management?
Data security management does not have a standard acronym or expanded full form. It refers to the processes, policies, and technologies used to protect information against unauthorized access, alteration, disclosure, loss, and destruction.
What are the five key elements of data security management?
Five essential elements are data classification, access control, encryption, monitoring, and backup and recovery. Together, they help organizations protect sensitive information and maintain access to essential business records.
What is the difference between data security and data privacy?
Data security focuses on protecting information from unauthorized access, modification, or loss. Data privacy concerns how personal information is collected, used, shared, retained, and processed.
How can small businesses improve data security management?
Small businesses should enable MFA, use a password manager, update software, limit access to sensitive files, encrypt important data, maintain tested backups, and train employees to report phishing.
How does AI affect data security management?
AI can help analyze security logs, detect unusual behavior, and prioritize potential threats. However, AI applications can also expose sensitive information through excessive permissions, insecure integrations, prompt injection, or unsafe data handling.