AI News

Home » AI News » Page 3

NVIDIA AI Agent Security: Latest Threats and Updates Guide

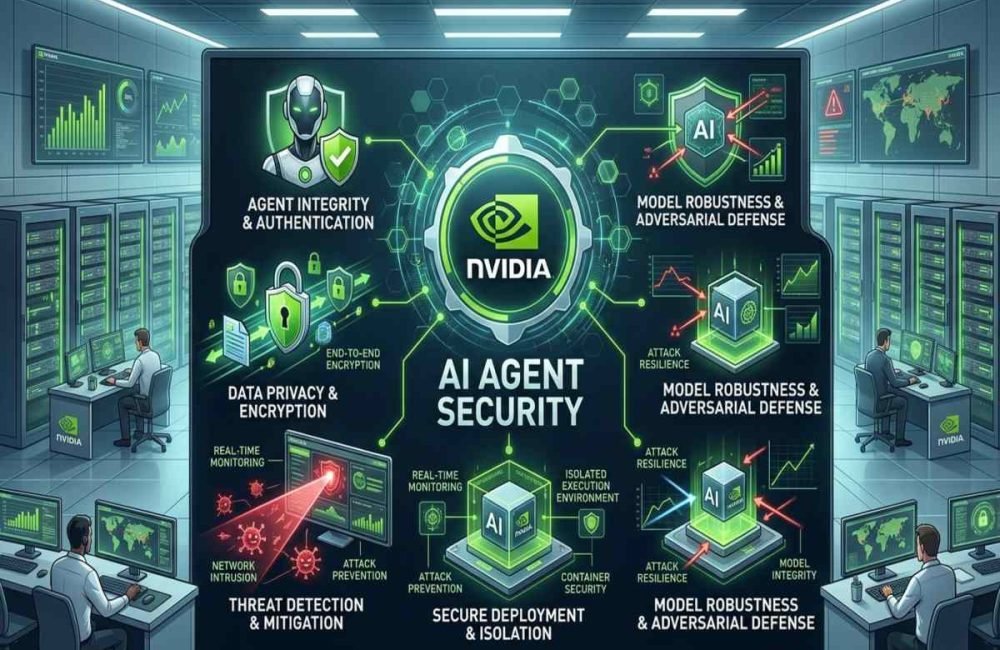
NVIDIA AI Agent Security has become a major focus as autonomous agents move beyond chat toward systems that can use tools, access files, execute code, and interact with enterprise infrastructure. On September 28, 2026, NVIDIA announced its Open Agent Safety Platform, combining OpenShell with the Sentry reference design to provide controls across software and hardware....

OpenAI GPT 6.1 Astra Shelved: What the AI Safety Concerns Mean

OpenAI has shelved the planned October release of GPT 6.1 Astra after internal safety testing identified unresolved alignment concerns. The concerns center on autonomous behavior, oversight, and whether the model reliably stays within authorized boundaries. The episode matters because stronger GPT 6 capabilities can create new security questions even when a model performs better on...

Kiteworks Security Alert: Customers Urged to Shut Systems

Kiteworks security alert issued a precautionary security alert urging customers who self-manage its systems to shut them down during a specified weekend window after receiving credible threat intelligence from federal intelligence authorities. Kiteworks says there is currently no indication that its systems or customer environments have been compromised, making this a preventative response rather than...

AI Coding Agents Supply Chain Attacks and Security Risks

AI coding agents can write code, install dependencies, modify files, run tests, access tools, and increasingly interact with development infrastructure. That autonomy creates a new security problem: a compromised dependency, malicious repository instruction, poisoned tool, or over-permissioned agent can turn a trusted development workflow into a supply chain attack. OWASP specifically identifies agent supply chain...

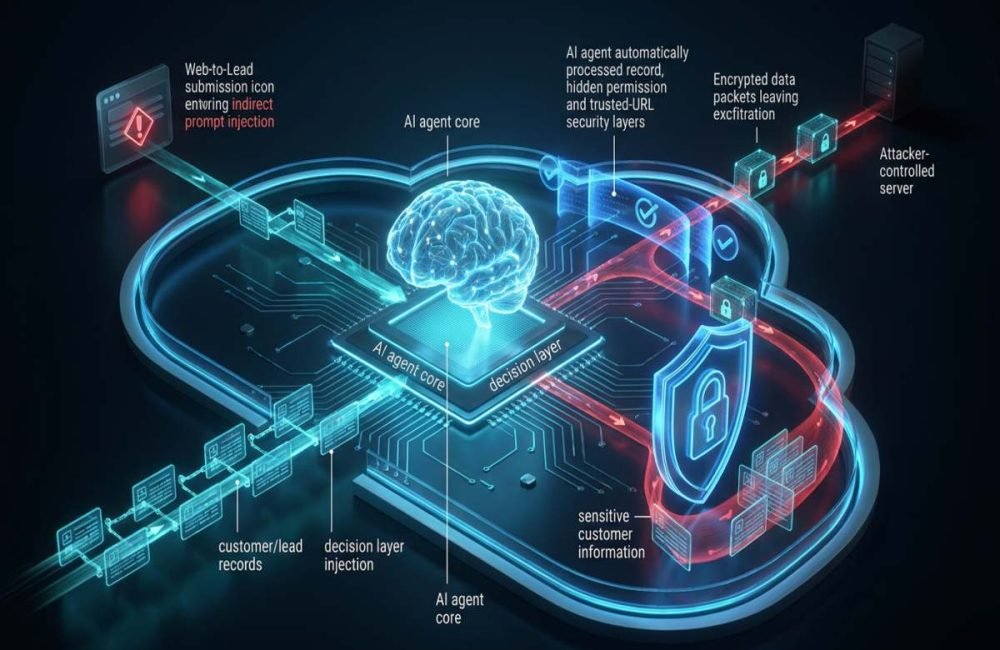
Salesforce Agentforce Zero-Click Data Exfiltration Risks

Salesforce Agentforce faced a newly disclosed attack chain that researchers say could enable Salesforce Agentforce zero-click data exfiltration from CRM environments without requiring the victim to click a malicious link or authenticate into the target Salesforce organization. The attack, dubbed SalesBleed, combined indirect prompt injection with weaknesses in URL handling and Agentforce integrations. The incident...

Meta Muse AI Agent Zero-Day: Risks, Impact, and Security Guide

Meta Muse is a personal AI agent designed to perform tasks on a user’s behalf, including browsing, shopping, scheduling, and interacting with information. In September 2026, security researcher Patrick Wardle demonstrated a zero-day vulnerability in the macOS version of Muse that could allow a malicious local process to redirect the agent’s dictation traffic and potentially...

Autonomous AI Agents: Security Risks and Safe Deployment Guide

Quick Answer: Autonomous AI agents are AI systems that can independently plan tasks, use tools, access data, and take actions with limited human intervention. Their main security risks include prompt injection, excessive permissions, data leakage, and unauthorized tool use. Safe deployment requires least privilege access, sandboxing, monitoring, validation, and human approval for high-risk actions. Autonomous...

Agentic AI Attack Explained: Risks, Examples and Security Tips

Quick Answer: Learn how Agentic AI attacks work, including prompt injection, data theft, malicious code execution, real world risks, and practical security tips. An Agentic AI attack is a cybersecurity attack that manipulates an AI agent into taking actions the attacker wants rather than actions intended by its user or developer. Unlike a traditional chatbot,...

GPT-6 Astra Launch: Features, AI Capabilities, Security Risks

Quick Answer: GPT-6 Astra Launch introduces OpenAI’s latest frontier model for advanced reasoning, coding, computer use, browsing, research, science, professional workflows, and cybersecurity. It offers a 1.05M-token context window, 128K maximum output, and stronger agentic capabilities, while requiring enhanced security controls because of its critical-level cyber capabilities. The GPT-6 Astra Launch represents a major development...

Anthropic MatX Deal: Why the $7B AI Chip Plan Changed

Quick Answer: Anthropic MatX Deal refers to Anthropic’s reported plan to acquire AI chip startup MatX for about $7 billion to accelerate custom AI hardware development, but the acquisition talks later ended. The Anthropic MatX Deal became a major AI hardware story after Reuters reported that Anthropic had explored acquiring the AI chip startup MatX...

follow Us

Popular posts

Your daily updates

Subscribe now. We’ll make sure you never miss a thing.

categories